AssessYourAttackSurface.PrioritizetheRisks.
Start with written authorization, named assets and safe testing limits. Prioritize findings, agree remediation owners and retest the scoped fixes; assessments cannot guarantee breach prevention.
Four Decisions Before Security Testing
Use your actual asset inventory and risk context. These are engagement steps, not breach statistics or a guarantee of protection.
Name assets, exclusions, test windows and written authorization.
Agree methods, access levels and evidence-handling rules.
Prioritize severity using reproducibility and business impact.
Verify scoped fixes and document residual risk.
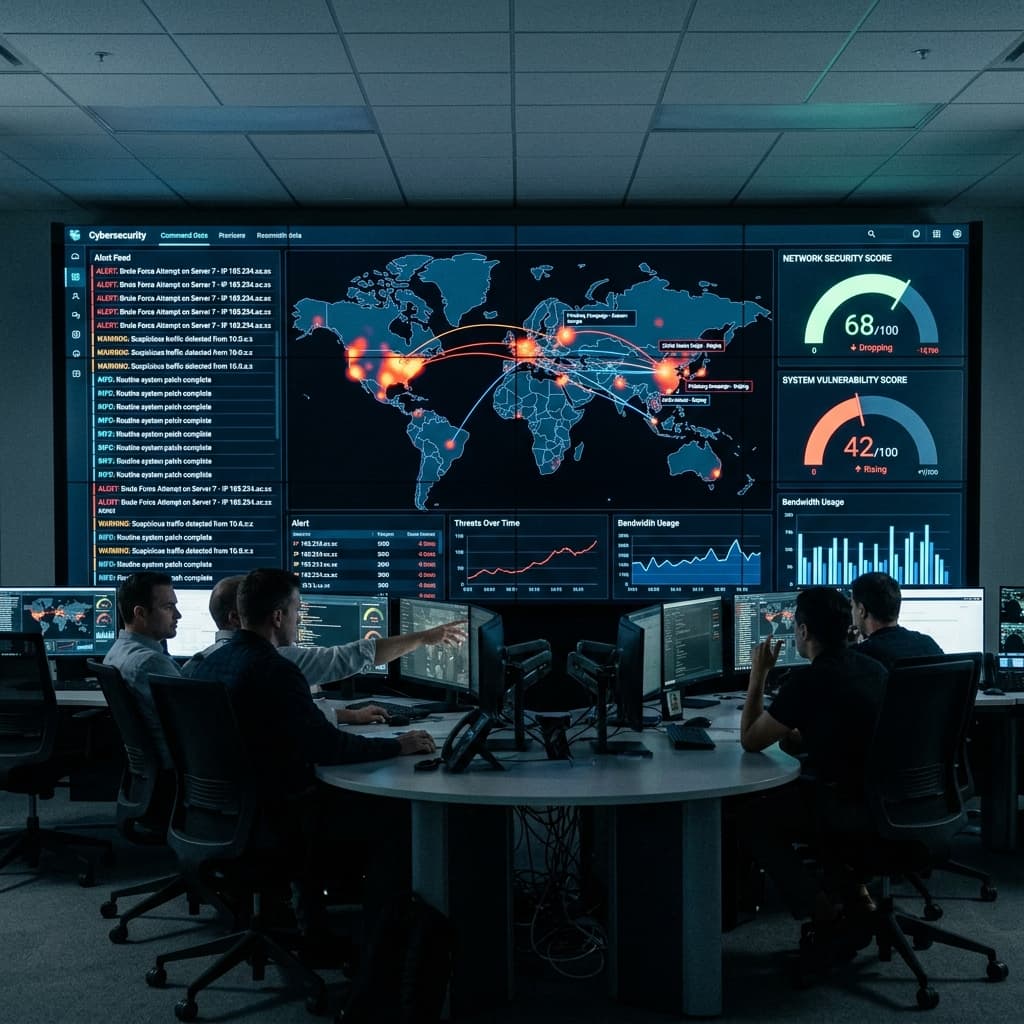
Illustrative Attack-Surface Review
Sample threat map only. Confirm which assets and methods are authorized; findings depend on access, testing time and the agreed scope.
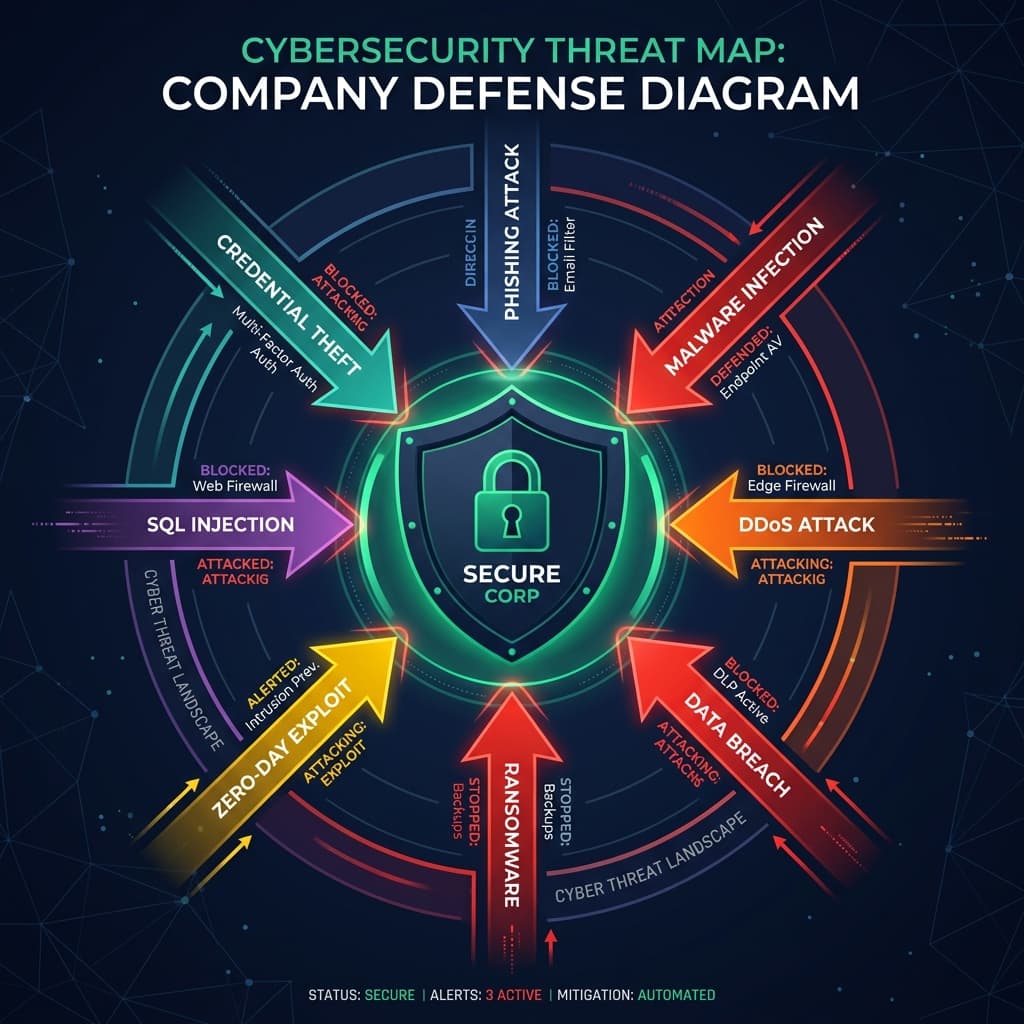
Our Cybersecurity Services
Penetration Testing
Authorized testing of named assets, with agreed methods, test windows, safe limits and a stop contact. Report reproducible findings and scoped retest results.
Zero-Trust Architecture
Review identity, least privilege and trust boundaries. Stage changes and test failure paths; no architecture eliminates all risk.
SAST & DAST Scanning
Configure selected code/runtime checks, severity triage and exception ownership. Automated scans do not replace a scoped manual review.
SOC2 Readiness Support
Scope gap analysis, control implementation and evidence preparation with the appointed independent auditor; no attestation or certification is promised.
Health Data Safeguards
Review authorized health-data flows, access controls and logging with the owner and qualified advisers; this is not regulatory approval.
Vulnerability Management
Agree asset coverage, scan cadence, severity thresholds, patch windows and retesting; document unpatched and accepted risks.
DDoS Protection
Evaluate edge controls, rate limits and escalation against realistic traffic; capacity and upstream dependencies still constrain availability.
Incident Response
Prepare scoped playbooks, escalation contacts and evidence handling. On-call hours and response terms require a separate agreement.
Compliance Readiness Support
Examples of readiness areas, subject to applicability and a written scope. Engineering support is separate from legal advice, independent audit, attestation or certification.
SOC2 Type I & II
Scope control mapping and evidence preparation with the appointed auditor; no attestation is issued by this page.
HIPAA
Review data flows and access safeguards with qualified advisers; legal applicability and approval are separate decisions.
ISO 27001
Assist with scoped security-control evidence; certification requires the appropriate independent assessment.
PCI-DSS
Agree the payment environment and evidence responsibilities with the relevant assessor; no certification is promised.
GDPR & CCPA
Document consent, retention and deletion requirements with the owner and advisers; this service is not legal advice.
NIST CSF
Map agreed risk-management activities and track gaps; framework alignment is not a certification claim.
Enterprise-Grade Security Tooling
Candidate tools for authorized testing only. Agree methods, licenses, access and evidence handling; tool names do not establish assessor qualifications or complete coverage.
Penetration Testing
- Burp Suite Pro
- Metasploit
- OWASP ZAP
- Nmap
- Wireshark
Vulnerability Scanning
- Nessus
- Qualys
- OpenVAS
- Snyk
- Trivy
Code Security
- SonarQube
- Semgrep
- CodeQL
- Checkmarx
Protection Layer
- AWS Shield
- Cloudflare WAF
- Fail2Ban
- ModSecurity
SIEM & Monitoring
- Splunk
- Elastic SIEM
- Wazuh
- IBM QRadar
Secrets Management
- HashiCorp Vault
- AWS Secrets Manager
- Azure Key Vault
The DevAura Security Engagement
A scoped assessment with explicit authorization and evidence limits; change approvals remain with your system owner.
Threat Assessment & Attack Surface Mapping
Confirm written authorization, asset inventory, exclusions, test windows and emergency stop contacts.
Architecture Security Review
Review agreed architecture, identity and data-flow controls with the supplied access; record visibility limits.
Penetration Testing (OWASP Methodology)
Use agreed non-destructive methods; capture reproducible evidence, severity and business impact within scope.
Vulnerability Remediation & Hardening
Assign remediation owners and priorities. Retest scoped fixes and record unresolved findings and residual risk.
Compliance Documentation & Continuous Monitoring
Handover findings, evidence and runbooks. Readiness support and monitoring are separately scoped; independent certification is not included.
Design sample — illustrative quote and attribution, not verified client feedback.
"I would want reproducible findings, a clear severity rationale and retest evidence for the assets we authorized."
Frequently Asked Questions
Agree an Authorized Security Assessment.
Define assets, access, test windows, exclusions and evidence requirements before quoting effort.
Enterprise security engineering across distributed architectures & global standards.